From the lab
Research
Security research and practical engineering guides. Read about AI attacks, application security, penetration testing, and the work of bringing AI into production.
Explore the benchmarksThe Counterweight newsletter
Stay updated.
Get new research, engineering guides, and benchmark releases in your inbox.
Service guides
Work with us
How much does a SaaS penetration test cost?
Build a useful budget from scope, tester time, reporting, and retesting. Includes a worked example and a checklist for comparing quotes.
Read the guide
SaaS penetration testing checklist: prepare your application
The accounts, permissions, test data, and operating arrangements that let a penetration test reach the workflows you need assessed.
Read the guide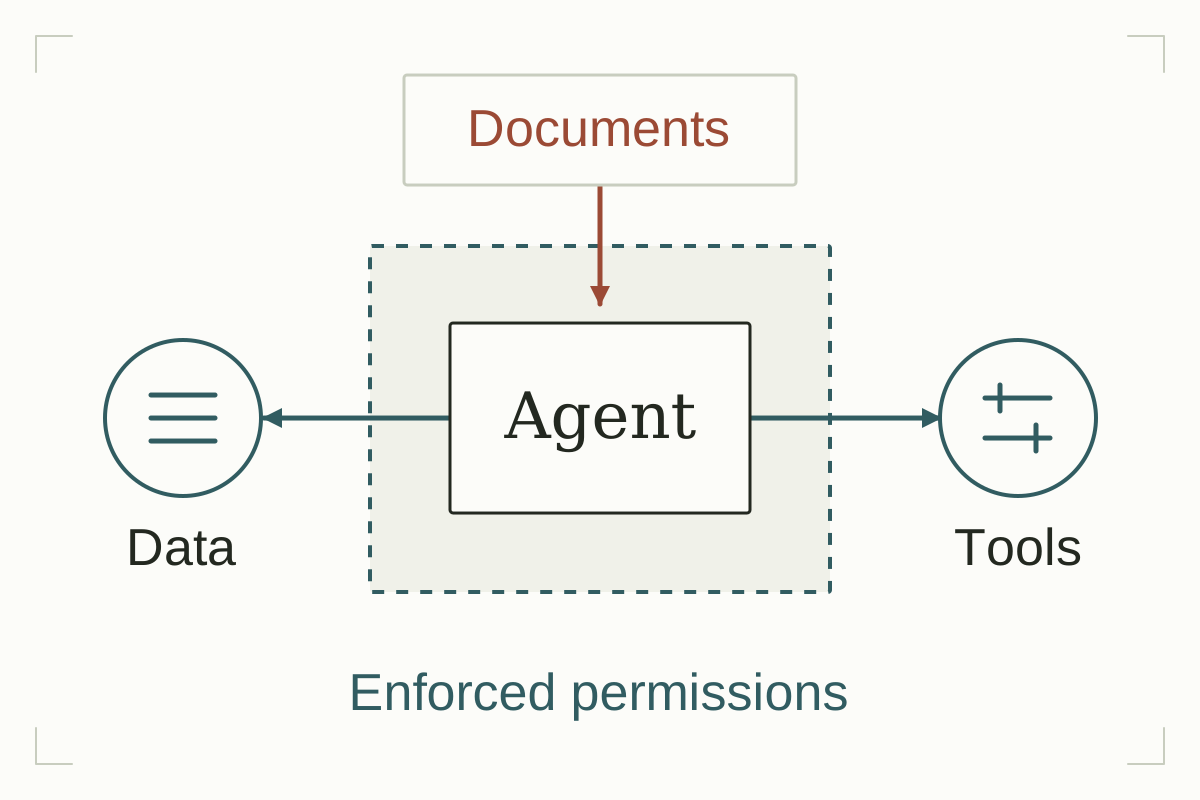
LLM penetration testing: what to test before launch
Scope an AI application assessment around data, identity, tools, and observable outcomes, with a practical test matrix for a support assistant.
Read the guide
Security review for AI-generated code: what to check before shipping
A review sequence for authentication, authorization, data handling, dependencies, and deployment changes in code written with AI assistants.
Read the guide
Secure code review vs. penetration testing: which do you need?
Choose an assessment based on the question you need answered, the access you can provide, and the evidence your team needs to act.
Read the guide
AI integration costs: budget for your first production workflow
Estimate implementation, evaluation, human review, and operating costs with a worked budget whose assumptions you can replace.
Read the guide
Showing 7–12 of 14
From the lab
Introducing Counterweight Labs
Seven cyber evaluations across enterprise networks, cloud and SaaS, product and release systems, and ransomware recovery.
Enterprise intrusion under active controls
A multi-host intrusion benchmark where EDR, identity controls, segmentation, and business services stay on.
Evicting a live enterprise intruder
The responder has to find every active session and persistence path while the network keeps serving its users.
Account takeover across cloud and SaaS
One stolen credential can cross source control, identity, cloud roles, OAuth grants, email, and deployment systems.
Ending a breach across cloud and SaaS
Containment has to revoke live access across several control planes without shutting down healthy workloads.
Compromising the software release path
The objective is a marked artifact that survives the real build, signing, registry, and downstream install path.
Showing 1–6 of 9