AI-generated security fixes: how to verify the vulnerability is gone
Review the security rule, test the original failure, and check adjacent paths. A plausible patch and a green test suite are only part of the evidence.
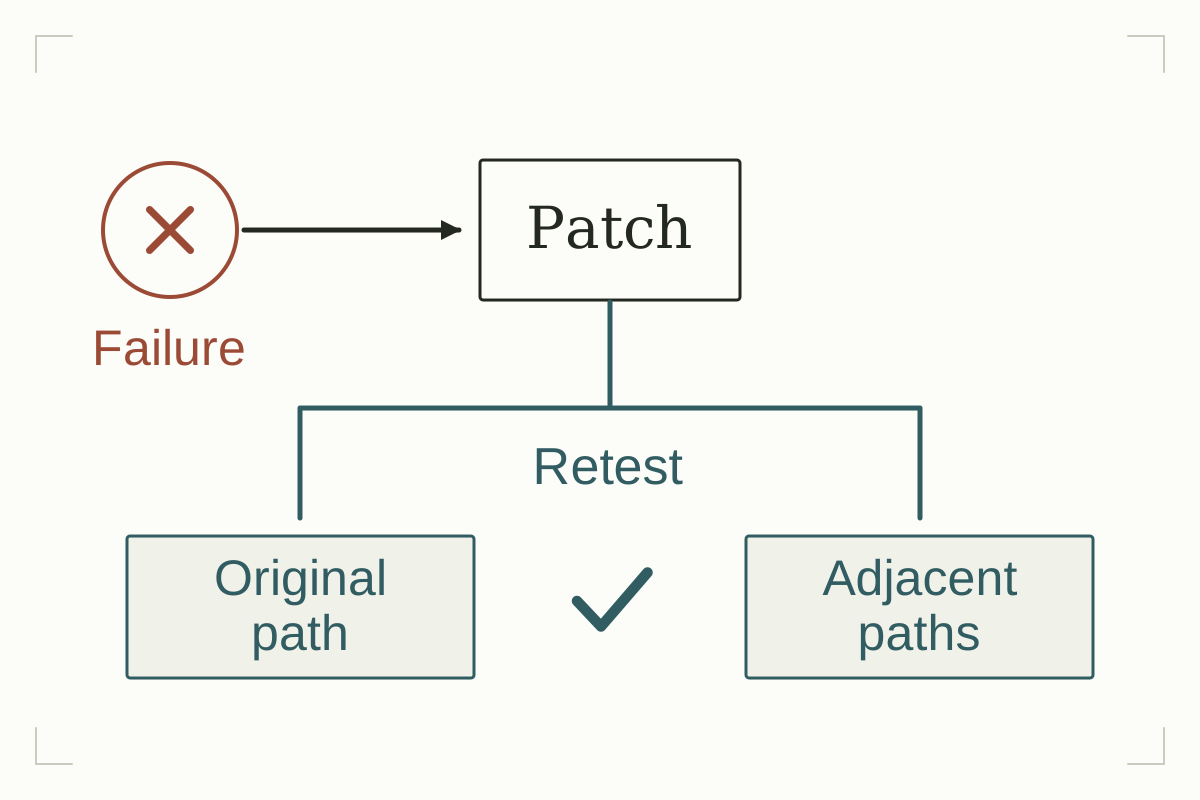
Verify an AI-generated security fix against the behavior that made the original finding exploitable. Establish a repeatable failure, define the security rule that should hold, inspect the patch, and run a regression check against both the vulnerable and corrected versions. Then test the neighboring paths the fix could have missed.
OWASP's Secure Coding with AI guidance warns about weakened tests, deleted assertions, and tests that reproduce a generator's own mistaken assumptions. It recommends independent verification of security-sensitive code and tests. Passing CI is useful evidence about the checks CI actually runs; inspect those checks before using the result to close a finding.Source: OWASP: secure coding with AI
Keep the original failure reproducible
Record the application version, test identity, relevant permissions, resource ownership, request, and observed result. Use synthetic data in a controlled environment. A finding described only as an authorization issue forces the patch author and reviewer to reconstruct the behavior, which creates room for them to fix different problems.
For an illustrative invoice API, the failure might be that a signed-in user from tenant A can read an invoice belonging to tenant B. The intended rule is that the user needs invoice-read permission in the invoice's tenant. Before reviewing code, agree on that rule and what response or side effect would count as a violation.
Review the decision the patch changes
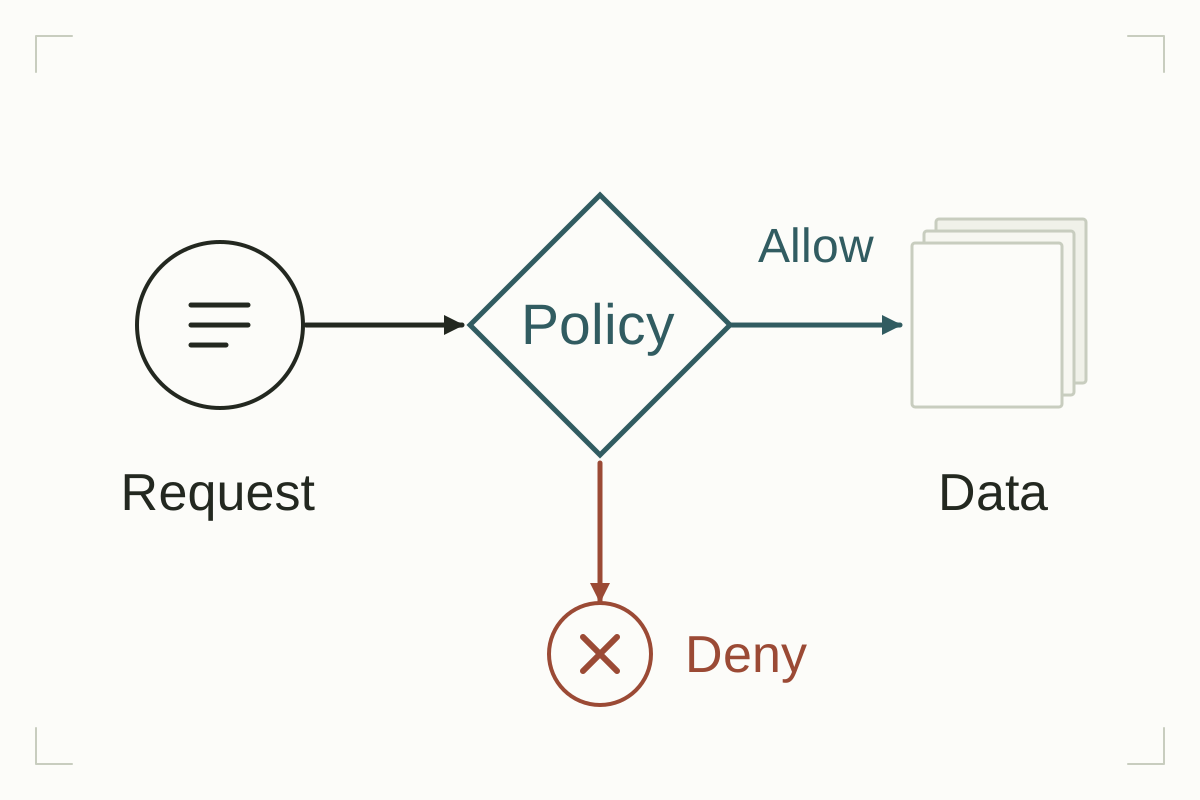
An agent may add a login check, compare a request parameter with another request parameter, or hide a download button. None of those changes necessarily enforces the intended resource-level rule. Trace the user identity and resource ownership back to trusted application state. Check that the server makes the decision on every affected access path.
Review the complete diff. Look for altered tests, new mocks, changed dependency versions, and configuration edits that affect execution. Ask why each change is needed for this finding. A small security patch becomes difficult to assess when unrelated cleanup hides which behavior is supposed to change.
Require a test that detects the old behavior
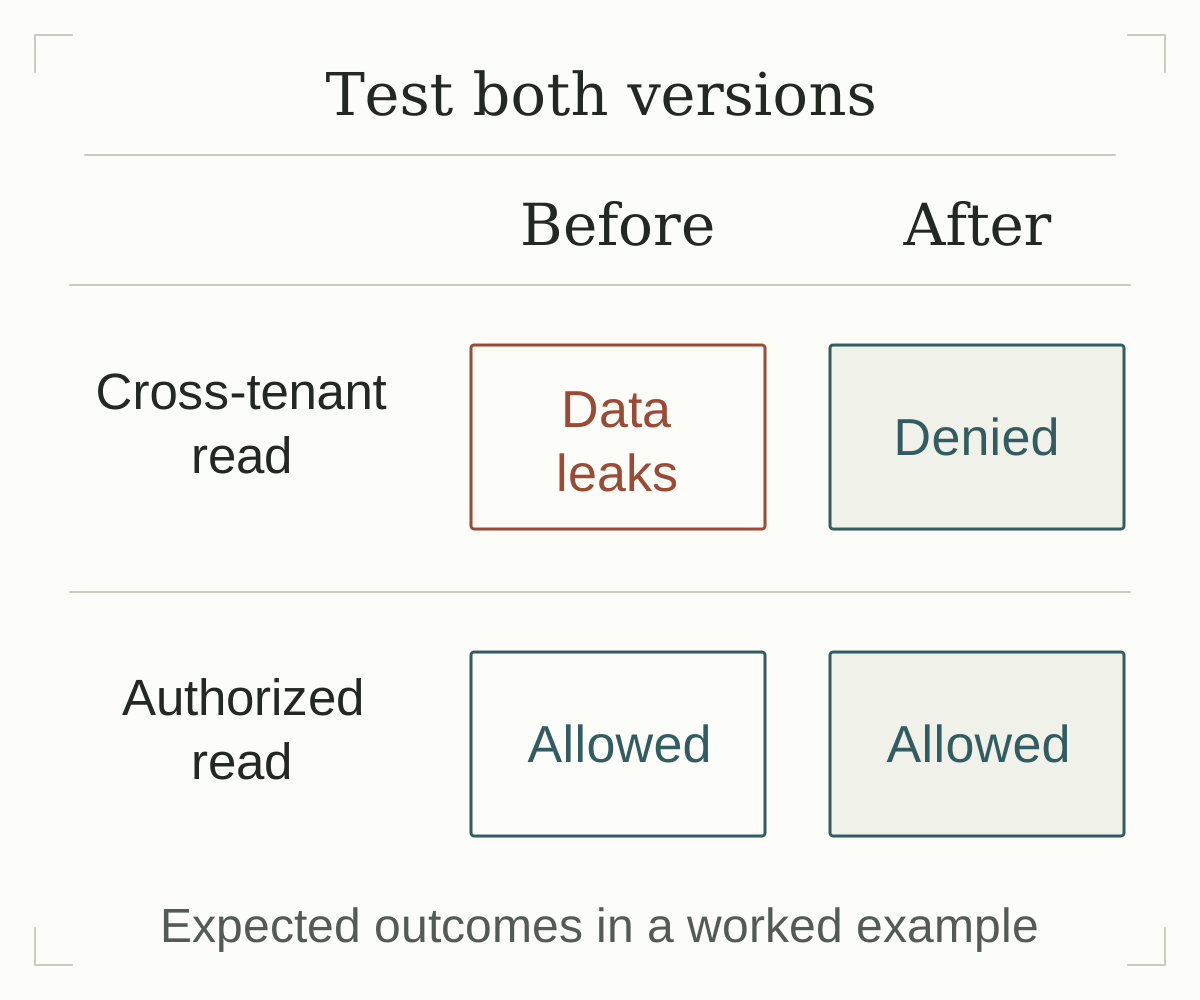
| Case | Vulnerable version | Corrected version |
|---|---|---|
| Tenant A reader requests tenant B invoice | Regression check detects unauthorized content | No invoice content or accessible artifact |
| Tenant A reader requests tenant A invoice | Allowed operation succeeds | Allowed operation still succeeds |
| Tenant A member lacks invoice-read permission | Record actual pre-fix behavior | Access denied |
| Export or background path requests tenant B invoice | Check the original and adjacent paths | The same resource boundary is enforced |
These are expected outcomes for a worked example, not results from a customer engagement. In a real retest, attach the requests and observations for the exact versions assessed. A test that reports success on the vulnerable version cannot establish that it detects this bug. It may still be useful for another purpose, but it needs revision before it serves as the regression check.
Inspect what the assertion observes. Checking only a status code can miss a response body containing protected data. Checking only the body can miss an export written to accessible storage. Use the security requirement to decide which outputs and side effects belong in the test.
Look for the same decision in adjacent paths
List the other ways the application performs the operation: another API version, a bulk endpoint, an export worker, a support tool, or a cached download. Review whether they share the corrected control. If they do not, decide whether they are within the finding's remediation scope or need separate tickets with explicit owners.
Also check the patch's failure behavior. If a permission lookup fails, does the operation remain denied? If the user loses access after a job is queued, does execution follow the documented policy? If resource ownership changes, is a cached access decision still acceptable? Select cases that correspond to the application's architecture instead of generating a large list of unrelated inputs.
Close the finding with a bounded statement
A closure note identifies the finding, fixed version, retested paths, observed outcome, and remaining coverage limits. For example: the direct and bulk invoice routes enforce the agreed tenant and permission checks in the tested build; the export worker is tracked separately because it was outside this retest.
Keep the regression test and its ownership after the finding is closed. If the application later replaces its authorization layer or export workflow, include this case in the review.
Sources
- OWASP: secure coding with AI cheatsheetseries.owasp.org
Bring the original finding, the proposed patch, and its tests. We can validate the remediation and retest the affected application paths.
Explore penetration testingContinue reading
Security review for AI-generated code: what to check before shipping
A review sequence for authentication, authorization, data handling, dependencies, and deployment changes in code written with AI assistants.
Read the guide
Security requirements for spec-driven development
Turn security requirements into enforceable behavior and negative tests before an AI coding agent starts implementation. A tenant-isolation example shows the full chain.
Read the guide